
Quiz
CCNA Security Chapter 6 Exam
Create a free account to finish this quiz
Save your progress and see your final score.
Already have an account? Sign in
Questions in this quiz (24)
1Refer to the exhibit. The Fa0/2 interface on switch S1 has been configured with the switchport port-security mac-address 0023.189d.6456 command and a workstation has been connected. What could be the reason that the Fa0/2 interface is shutdown?
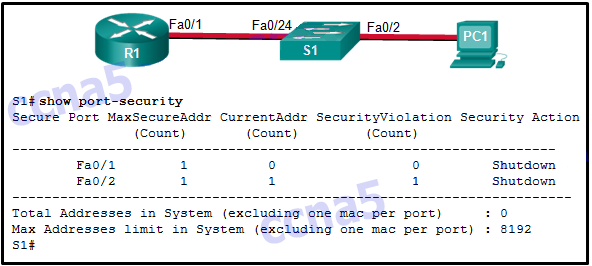
- AThe connection between S1 and PC1 is via a crossover cable
- BThe Fa0/24 interface of S1 is configured with the same MAC address as the Fa0/2 interface
- CS1 has been configured with a switchport port-security aging command
- DThe MAC address of PC1 that connects to the Fa0/2 interface is not the configured MAC address
2Two devices that are connected to the same switch need to be totally isolated from one another. Which Cisco switch security feature will provide this isolation?
- APVLAN Edge
- BDTP
- CSPAN
- DBPDU guard
3Which two functions are provided by Network Admission Control?
- Aprotecting a switch from MAC address table overflow attacks
- Benforcing network security policy for hosts that connect to the network
- Censuring that only authenticated hosts can access the network
- Dstopping excessive broadcasts from disrupting network traffic
- Elimiting the number of MAC addresses that can be learned on a single switch port
4Which spanning-tree enhancement prevents the spanning-tree topology from changing by blocking a port that receives a superior BPDU?
- ABDPU filter
- BPortFast
- CBPDU guard
- Droot guard
5Which security feature should be enabled in order to prevent an attacker from overflowing the MAC address table of a switch?
- Aroot guard
- Bport security
- Cstorm control
- DBPDU filter
6In what situation would a network administrator most likely implement root guard?
- Aon all switch ports (used or unused)
- Bon all switch ports that connect to a Layer 3 device
- Con all switch ports that connect to host devices
- Don all switch ports that connect to another switch
- Eon all switch ports that connect to another switch that is not the root bridge
7What component of Cisco NAC is responsible for performing deep inspection of device security profiles?
- ACisco NAC Profiler
- BCisco NAC Agent
- CCisco NAC Manager
- DCisco NAC Server
8What is the role of the Cisco NAC Manager in implementing a secure networking infrastructure?
- Ato define role-based user access and endpoint security policies
- Bto assess and enforce security policy compliance in the NAC environment
- Cto perform deep inspection of device security profiles
- Dto provide post-connection monitoring of all endpoint devices
9What is the role of the Cisco NAC Server within the Cisco Secure Borderless Network Architecture?
- Aproviding the ability for company employees to create guest accounts
- Bproviding post-connection monitoring of all endpoint devices
- Cdefining role-based user access and endpoint security policies
- Dassessing and enforcing security policy compliance in the NAC environment
10What is the role of the Cisco NAC Guest Server within the Cisco Borderless Network architecture?
- AIt defines role-based user access and endpoint security policies.
- BIt provides the ability for creation and reporting of guest accounts
- CIt provides post-connection monitoring of all endpoint devices
- DIt performs deep inspection of device security profiles
11Which three functions are provided under Cisco NAC framework solution? (Choose three.)
- AVPN connection
- BAAA services
- Cintrusion prevention
- Dscanning for policy compliance
- Esecure connection to servers
- Fremediation for noncompliant devices
12Which feature is part of the Antimalware Protection security solution?
- Afile retrospection
- Buser authentication and authorization
- Cdata loss prevention
- Dspam blocking
13What security countermeasure is effective for preventing CAM table overflow attacks?
- ADHCP snooping
- BDynamic ARP Inspection
- CIP source guard
- Dport security
14What is the behavior of a switch as a result of a successful CAM table attack?
- AThe switch will forward all received frames to all other ports
- BThe switch will drop all received frames
- CThe switch interfaces will transition to the error-disabled state
- DThe switch will shut down
15What additional security measure must be enabled along with IP Source Guard to protect against address spoofing?
- Aport security
- BBPDU Guard
- Croot guard
- DDHCP snooping
16What are three techniques for mitigating VLAN hopping attacks? (Choose three.)
- ASet the native VLAN to an unused VLAN
- BDisable DTP
- CEnable Source Guard
- DEnable trunking manually
- EEnable BPDU guard
- FUse private VLANs
17What two mechanisms are used by Dynamic ARP inspection to validate ARP packets for IP addresses that are dynamically assigned or IP addresses that are static? (Choose two.)
- AMAC-address-to-IP-address bindings
- BRARP
- CARP ACLs
- DIP ACLs
- ESource Guard
18What protocol should be disabled to help mitigate VLAN hopping attacks?
- ASTP
- BARP
- CCDP
- DDTP
19What network attack seeks to create a DoS for clients by preventing them from being able to obtain a DHCP lease?
- ADHCP spoofing
- BCAM table attack
- CIP address spoofing
- DDHCP starvation
20What is the only type of port that an isolated port can forward traffic to on a private VLAN
- Aa community port
- Ba promiscuous port
- Canother isolated port
- Dany access port in the same PVLAN
21Which STP stability mechanism is used to prevent a rogue switch from becoming the root switch?
- ASource Guard
- BBPDU guard
- Croot guard
- Dloop guard
22How can a user connect to the Cisco Cloud Web Security service directly?
- Athrough the connector that is integrated into any Layer 2 Cisco switch
- Bby using a proxy autoconfiguration file in the end device
- Cby accessing a Cisco CWS server before visiting the destination web site
- Dby establishing a VPN connection with the Cisco CWS
23What security benefit is gained from enabling BPDU guard on PortFast enabled interfaces?
- Aenforcing the placement of root bridges
- Bpreventing buffer overflow attacks
- Cpreventing rogue switches from being added to the network
- Dprotecting against Layer 2 loops
24Which mitigation technique would prevent rogue servers from providing false IP configuration parameters to clients
- Aimplementing port-security on edge ports
- Bimplementing port security
- Cturning on DHCP snooping
- Ddisabling CDP on edge ports
Information
- Description
- CCNA Security Chapter 6 Exam
- Author
- d94829 d94829
- Language
- English
- Views
- 649
- Tags
- Rating
- No ratings yet Rate this quiz