
Flashcards
Misc Concepts in Network Security
Cards in this deck (31)
- 1Livenessan assurance that a principal sent a particular message within an acceptably
recent timeframe - 2Freshnessassurance to a principal that a message has not been used previously and
originated within an acceptably recent timeframe - 3ISO-7498-2 Security Services (5)Authentication (entity Auth. & Data origin Auth.)
Access Control
Confidentiality
Integrity
Non-Repudiation - 4ISO 7498-2 Confidentialitycategorize Confidentiality as;
Connection Confidentiality (all connections)
Connection-less confidentiality (single session/packet)
Selection Field Confidentiality (some fields encryption)
Traffic Flow Confidentiality (Traffic type protection) - 5ISO-7498-2 Integrity (against active threats)Integrity with Recovery (detects violation & trying to recover)
Integrity without Recovery (detects violation without trying to recover)
Selective field Integrity (part of data has integrity)
Connection-less Integrity (validation of SW download)
Selective Field Connection-less (as above but selective) - 6ISO 7498-2 Non-RepudiationNon Repudiation of Origin (Denying Data Sent)
Non Repudiation of Delivery (Denying date received) - 7Security Mechanisms (13) that implements the Security Services (5)Specific Security Services (8)
Pervasive Security Services (5) [ support provision of other sec services] - 8Specific Security Mechanisms (8)Encipher
Data Integrity
Digital Signatures
Access Control
Authentication exchange
Traffic Padding
Routing Control
Notarization (3rd party) - 9Pervasive Security MechanismsTrusted Function
Security Labels
Event Detection
Audit Trail
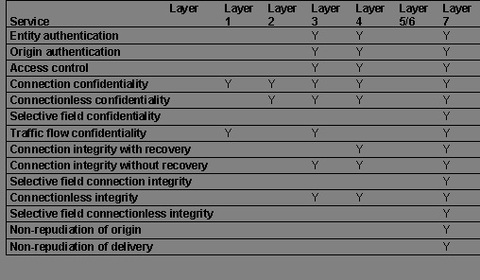
Recovery - 10Layers vs. Servcies
- 11ARPTranslate Specific IP Address to MAC
- 12ARP SpoofingFalsify IP (Send G-ARP to direct traffic to attacker PC)
MAC Flooding (makes switch act like a hub by filling ARP Table, or DOS for the switch ) - 13Defenses Against ARP SpoofingStatic Translation between Port & MAC
Prevent GARP to be sent
limit the number of MAC at each port - 14WAN Security MeasuresPartition networks physically
Partition networks logically
Data Confidentiality & Encryption - 15ISO 7498-2 Network Management SecurityManagement of Security
Security of Management - 16SNMPat least 1X network management station & number of network elements
they support;
configuration management
event logging
accounting - 17SNMP OperationsSET
GET
TRAP - 18SNMP ThreatPossibility that one device might act with the authority of another device
- 19SNMP Security Security servicesAuthentication Service (Community name)
Access Control (Defines Community access rights) - 20SNMP V3Network managers should have UN & PSW for Authentication
each SNMP entity has Identity
Confidentiality - 21Fundamental ThreatsData Leakage
Integrity Violation
DOS
illegitimate use - 22Primary enabling ThreatsMasquerading (Entity claims itself another entity)
Trojan Horse
Trapdoor (software function hidden to pass security policy)
Bypass Control
Authorized violation (e.g. XSS) - 23OSI 7 layersApplication, Presentation, Session, Transport, Network, Data link & Physical
- 24Session layer functionestablishes session, control session parameters (half duplex, full duplex...), synch done at this layer
- 25Presentation Layer FunctionPrepares the data to be ready for other layers and recipient
Compression & Encryption is done here - 26Transport Layerresponsible for moving the App from one PC to another, establishes virtual connection to specify which application to be used
Guarantee messages revival - 27OSI Layering AdvantagesAllows protocol designers and implementers to divide
up the problem and focus on solving one piece of the problem at a
time. - 28Services vs. ProtocolsService is provided by one layer to the other one above it
Protocol is specifying how service is implemented - 29ISO 7498-2Dealing specifically with the security of
communications networks - 30ISO-7498-2 stages life cycleDefine a security policy.
Analyze the security threats according to the policy.
Define the security services to meet threats.
Define the security mechanisms to provide services.
Provide on-going management of security. - 31RulesDescribes how the system should work and configured, there are two types; identity based (based on the identity) & rule based (based on the configured rules)
Information
- Description
- Net SEC Flashcards on Misc Concepts in Network Security, created by Moh.enab on 10/05/2013.
- Created by
- Moh.enab
- Views
- 90
- Tags
- Rating