
Mind map
Azure AZ500
Map content
Azure AZ500
50 regions & 140 Countries
- Region Pairs (east or west etc..) - always good to check which patches have been applied
Azure Resource Groups
- Containers : where you can group all services like DB, apps.
Networking: VNets
- Subnet 1
- Subnet 2 etc...
- Isolated networks
- Internet access
- Traffic Filters (NSG) - Routing
- Internet access
Virtual Machines set up:
- HDD/CPU?Memory > Hardware > Hypervisor > VM
- VM = OS + APPS
- HDD/CPU?Memory > Hardware > Hypervisor > VM
App + DB Services
- App Services: - Web Apps - Mobile Apps - Functions - Logic Apps - Containers (Azure Container Services (AKS))
- DB Services: -SQL - AzureSQL - Cosmos DB
- Storage: -Blob -table -file -messages
- Other: -Machine Learning and AI - IoT -Identity (AD) -Operations -Security
SECURITY
- CIA
- Confidentiality: Principle of least privelege - RESTRICT ACCESS - INFO INCLUDES USER PASSWORDS, CERTIFICATES EMAIL
- INTEGRITY : prevention of unauthorised changes to info DATA In REST or DATA in TRANSITION
- AVAILABILITY: - Ensure services are available - HIGH AVAILABILITY and DR
- LAYERS
- DATA Layer
- Application Layer
- Compute (OS infarastructure)
- Network layer Security
- Perimeter (of network) security
- Identity & Access :
- Physical Security (data centres etc..)
- Building Access etc..
- Control access to Infrastructure: Authenticate (Prove who you are) - Authorisation - AUDIT events and changes
- Physical Security (data centres etc..)
- PROTECT NETWORK : DDOS Protection - FIREWALLS -
- Identity & Access :
- Only allow what is required - Deny by Default - limit internet and comms - SEPERATE VLANS etc..
- Perimeter (of network) security
- HARDENING OS / VM's -implement ENDPOINT protection - Control Access
- Network layer Security
- Ensure apps are secure - Make security requirements for all new dev (secure by default etcc)
- Compute (OS infarastructure)
- Responsible for data is secure while in transit and in rest : ALMOST ALL ATTACKS WANT DATA
- Application Layer
- DATA Layer
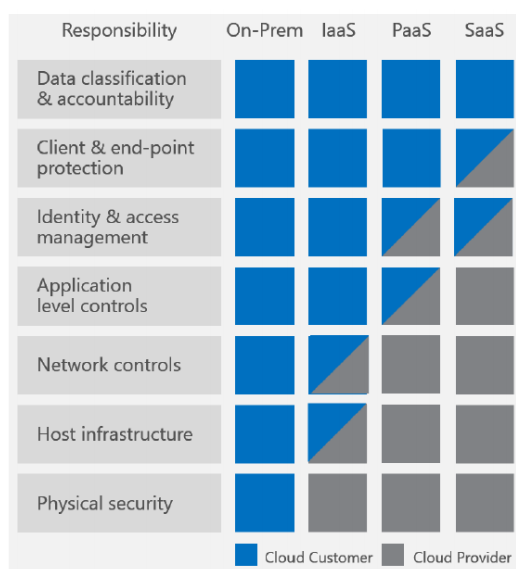
- Security Responsibility of layers
- USER RESPONSIBLE ALWAYS: DATA - ENDPOINTS - ACCOUNTS - ACCESS MGT
- Microsoft Trust Center
- In depth details of MS Pen tests, SOC, AUDIT REPORTS etc..
- COMPLIANCE MANAGER: AZURE Tool to Proactive RISK ASSESMENTprepare AUDIT Reports
- CIA
AZURE AD
- FEATURES: ENTERPRISE IDENTITY SOLUTION - SINGLE SIGN_ON - MULTIFACTOR AUTH (MFA) - SELF SERVICE
- AD CONNECT:
- Synchronization services : CREATING USER GROUPS , SYNC ID INFO with ONSITE AD
- Filtering: limit which objects are syncd (default is users, groups etc)
- Password Hash Sync : This sync password hash from On premises AD to Azure AD - so users can use local passwords with azure - this also copies local AD Pwd policy to Azure AD
- Password SYNC: ensures user passwords are same on both directories (local AD DS and Azure AD)
- Pwds Hash on 2 locations /syncd
- Passthrough Authentication: easy method to keep users and passwords aligned > when user logs into Azure AD, the request is forwarded to local AD DS. essentially single source
- Passwords only on LOCAL AD
- AD F FEDERATION Services : Fully federate accross AD DS and Azure AD along with other services (i.e. SNOW)
- Password SYNC: ensures user passwords are same on both directories (local AD DS and Azure AD)
- Password Writeback: allows users to reset PWD in cloud and thsi will change also in local AD
- Device writeback: allows conditional access configured in Azure AD to be written back to local AD
- Prevent Accidental deletes : by default only allows 500 deletes per run
- Automatic Upgrade : Ensure Azure AD connect is auto updated by default
- AD FEDERATION SERVICES (OPTIONAL) : CONFIG HYBRID ENV : for more complex environments, MFA 3rd party etc
- HEALTH MONITORING: CENTRAL LOCATION TO VIEW DOMAIN HEALTH
- Synchronization services : CREATING USER GROUPS , SYNC ID INFO with ONSITE AD
- PIM (Privileged Identity Management)
- Privileged users e.g global admin - Enable on demand admin access -View Admin history - setup alerts - require approvals
- Actiation process : Users need additional Authentication (MFA) - Need approvals -REQUIRE Azure AD P2 License
- Privileged users e.g global admin - Enable on demand admin access -View Admin history - setup alerts - require approvals
Images and files in the map
Information
- Description
- Information Technology Mind Map on Azure AZ500, created by T Ch on 14/04/2020.
- Created by
- T Ch · Apr 2020
- Updated
- Apr 21, 2020
- Views
- 4
- Rating