
Mind map
System Threats
Map content
System Threats
Malware
- Malicious software which is specifically designed to disrupt, damage, or gain authorized access to a computer system.
- It can slow down your computer or make it crash. A worm will slow down the internet connection. Files may be deleted, corrupt or encrypted. . Malware might be designed to record the keys that you press on your keyboard, for example, creating a text log that your computer sends to a hacker periodically. The hacker then scans the text log, looking for passwords that he can use to access your email or bank accounts.
- Preventing malware - Strong security software (firewall, spam filter, anti-virus(Update regulary), anti-spyware, anti-spam) - Enable OS updates - Staff training: caution opening attachments - Back up files regularly
- Malicious software which is specifically designed to disrupt, damage, or gain authorized access to a computer system.
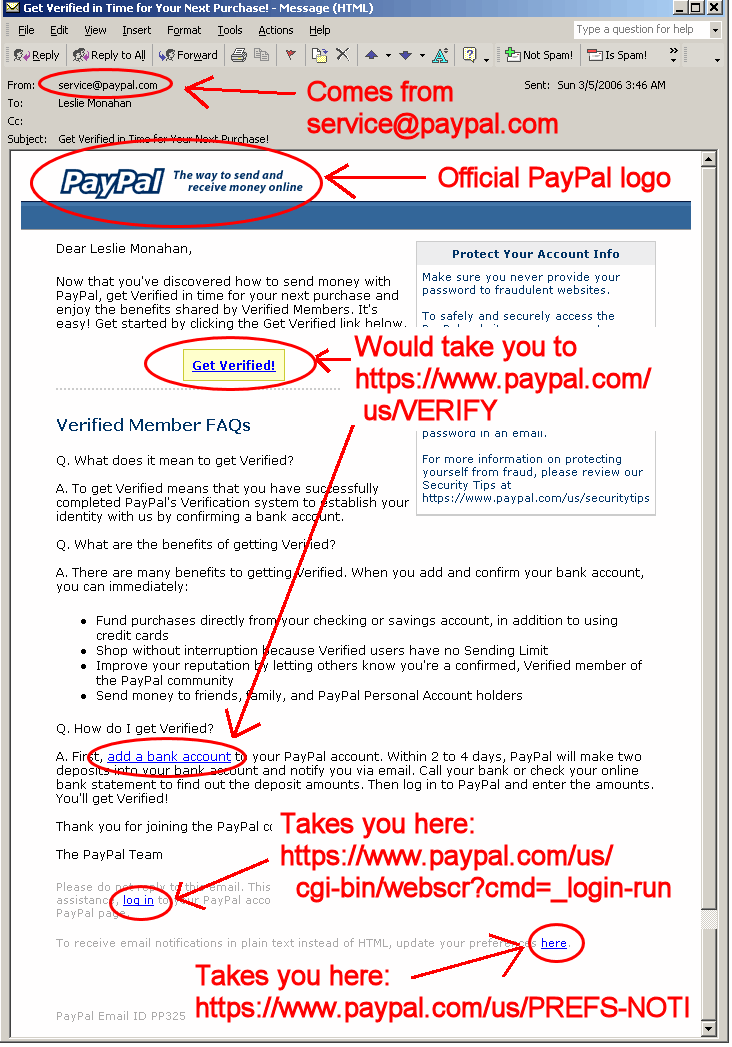
Phishing
- Phishing is an online fraud technique used by criminals to entice you to disclose personal information such as usernames, passwords and credit card details by disguising as a trustworthy entity in an electronic communication
- The effects of phishing Accessing a victim’s account and withdraw money or purchase merchandise or services. Open new bank or credit-card accounts in a victim’s names, and use the new account to cash illegitimate checks or purchase merchandise. Gaining access high-value corporate data. Financial services can blacklist institutions, resulting in reputational damage.
- Preventing phishing .. Strong security software (firewall, spam filter, anti-virus, anti-spam). Staff training: awareness of spotting fake websites & emails. Staff training: never disclose personal or financial information. Staff training: disable pop-ups.
- The effects of phishing Accessing a victim’s account and withdraw money or purchase merchandise or services. Open new bank or credit-card accounts in a victim’s names, and use the new account to cash illegitimate checks or purchase merchandise. Gaining access high-value corporate data. Financial services can blacklist institutions, resulting in reputational damage.
- Phishing is an online fraud technique used by criminals to entice you to disclose personal information such as usernames, passwords and credit card details by disguising as a trustworthy entity in an electronic communication
Brute Force Attack
- A brute force attack is a trial and error method used by programs to decode encrypted data such as passwords or Data Encryption Standard (DES) keys, through exhaustive effort rather than employing intellectual strategies.
- The effects of brute force • Theft of data. Access to corporate and private computer systems.
- Preventing brute force attacks • Network lockout policy: locks out after a number of tries. Staff training: using effective passwords that contain symbols and numbers. Challenge response tests e.g. reCAPTCHA – user has to look at a picture and answer a question.
- The effects of brute force • Theft of data. Access to corporate and private computer systems.
- A brute force attack is a trial and error method used by programs to decode encrypted data such as passwords or Data Encryption Standard (DES) keys, through exhaustive effort rather than employing intellectual strategies.
Preventing SQL injection - Validation of input fields. - Using parameterised queries. - Using database permissions. - Penetration testing.
- Effects of SQL injection • Contents of the database can be output, revealing data that otherwise would be hidden. • Data in the database can be amended and deleted. • New rogue records can be added.
- SQL injection is a code injection technique, used to attack data-driven applications. If a database application has not been coded in a secure way, code can be entered into text boxes, and will be executed by the server.
- SQL injection
- SQL injection is a code injection technique, used to attack data-driven applications. If a database application has not been coded in a secure way, code can be entered into text boxes, and will be executed by the server.
- Effects of SQL injection • Contents of the database can be output, revealing data that otherwise would be hidden. • Data in the database can be amended and deleted. • New rogue records can be added.
Denial of Service Attack
- In computing, a denial-of-service attack (DoS attack) is a cyber-attack where the perpetrator seeks to make a machine or network resource unavailable to its intended users by temporarily or indefinitely disrupting services of a host connected to the Internet.
- • Revenue losses: downtime affects profits. Based on industry surveys, the average cost of downtime is over £4000/minute • Productivity Loss: when critical network systems are shut down, your workforce’s productivity comes to a halt. • Reputation Damage: your brand suffers if customers can’t access your site or become casualties of a data breach.
- • Strong security software (firewall). • Packet filters on routers. • Configuration of the webserver. • Good network policy: audits, logs, monitoring.
- • Revenue losses: downtime affects profits. Based on industry surveys, the average cost of downtime is over £4000/minute • Productivity Loss: when critical network systems are shut down, your workforce’s productivity comes to a halt. • Reputation Damage: your brand suffers if customers can’t access your site or become casualties of a data breach.
- In computing, a denial-of-service attack (DoS attack) is a cyber-attack where the perpetrator seeks to make a machine or network resource unavailable to its intended users by temporarily or indefinitely disrupting services of a host connected to the Internet.
Preventing data interception and theft • Strong encryption. • Using virtual networks. • Staff training: use of passwords, locking and portable storage devices. • Network forensics.
- Effects of data interception and theft • Discovering username and password credentials. • Gaining access to systems. • Disclosure of corporate data. • Theft of data.
- Data Theft Definition. The unauthorized taking or interception of computer-based information. Data theft is the act of stealing computer-based information from an unknowing victim with the intent of compromising privacy or obtaining confidential information.
- Data interception and theft
- Data Theft Definition. The unauthorized taking or interception of computer-based information. Data theft is the act of stealing computer-based information from an unknowing victim with the intent of compromising privacy or obtaining confidential information.
- Effects of data interception and theft • Discovering username and password credentials. • Gaining access to systems. • Disclosure of corporate data. • Theft of data.
Images and files in the map
Information
- Description
- GCSE Computing Mind Map on System Threats, created by Josh Allen on 05/05/2017.
- Created by
- Josh Allen
- Views
- 0
- Rating